Everything You Need to Know About DDoS Attacks
Navigating the modern internet requires confronting an ongoing wave of digital hazards. From routine news bulletins detailing massive corporate data compromises to silent malware infections harvesting sensitive credentials, online security vulnerabilities seem permanent. Because individuals and enterprises continually transmit critical records across the web, including payment data and Social Security numbers, malicious actors remain motivated to probe network infrastructure for any exploitable opening.
Among the wide variety of modern network hazards, the distributed denial of service attack represents one of the most disruptive yet widely misunderstood operations. Anyone maintaining a server, launching an online storefront, or administering an organization-wide email system faces exposure to these aggressive digital bottlenecks. Developing a thorough grasp of how these traffic floods operate, how to recognize their onset, and how to structure resilient hosting environments is fundamental to preserving operational stability.
Key takeaways
- A distributed denial of service attack seeks to disable a server by flooding it with illegitimate network requests from thousands of connected machines.
- Major server outages for the top five eCommerce websites across the United States can cost approximately $3.5 million per hour in lost revenue and operational impact.
- Modern attack volumes frequently reach several hundred gigabytes per second, easily overwhelming standard or unmanaged defense software.
- Targets span every scale and sector, ranging from major corporate platforms to modest local non-profit organizations.
- Effective mitigation relies on load balancing, upgraded hosting protections, continuous software patching, and rapid communication with hosting engineers.
The Mechanics and Economic Toll of Traffic Floods
At its core, a denial of service operation seeks to exhaust computational capacity until an online platform can no longer interact with authentic visitors. Rather than breaching a perimeter to steal intellectual property or exfiltrate private records, these operations create digital blockades. When an attacker floods a target network with excessive, artificial inquiries, the underlying host dedicates all its processing queues to evaluating bad data, leaving legitimate transactions unfulfilled.
The financial consequences of unexpected downtime accumulate immediately. Platforms relying on direct consumer purchases or steady ad impressions forfeit revenue with every elapsed minute of unresponsiveness. When shoppers cannot load inventory pages, complete purchase orders, or log into their customer profiles, commercial activity halts. Research highlights the extreme magnitude of these failures, demonstrating that major server outages for the top five eCommerce sites in the United States total about $3.5 million per hour. Beyond instantaneous transaction losses, prolonged outages erode brand credibility, alienate recurring clients, and trigger costly engineering scrambles.
The scale of these campaigns continues to widen dramatically. Network operators now regularly log malicious bursts measuring several hundred gigabytes per second. This expanding scale invalidates legacy prevention utilities, which were architected during an era when incoming volumetric traffic was significantly smaller. Furthermore, bad actors do not limit their efforts to well-funded enterprises; public agencies, community charity portals, and small non-profits are assaulted with identical frequency whenever unpatched vulnerabilities are exposed.
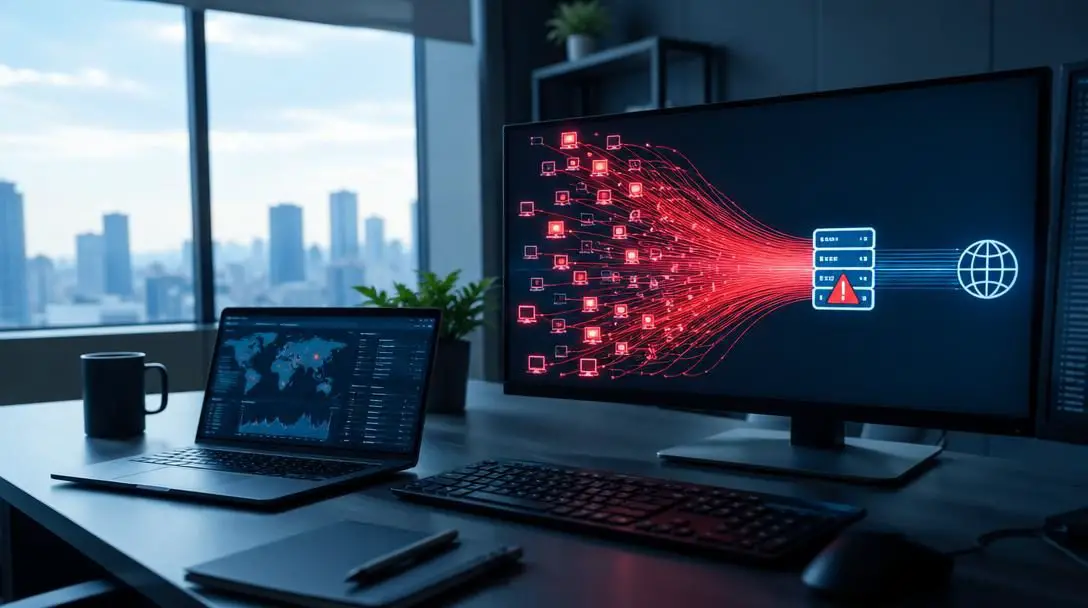
When an artificial traffic flood consumes every shred of server bandwidth, genuine customers are shut out completely while financial losses mount by the minute.
How Distributed Networks Coordinate an Assault
The foundational danger of these campaigns lies in the distinction between a local assault and a distributed operation. While an attack from an isolated computer can be neutralized by blocking an individual network address, a distributed campaign leverages diverse devices distributed across global networks.
Compromising Web-Connected Devices
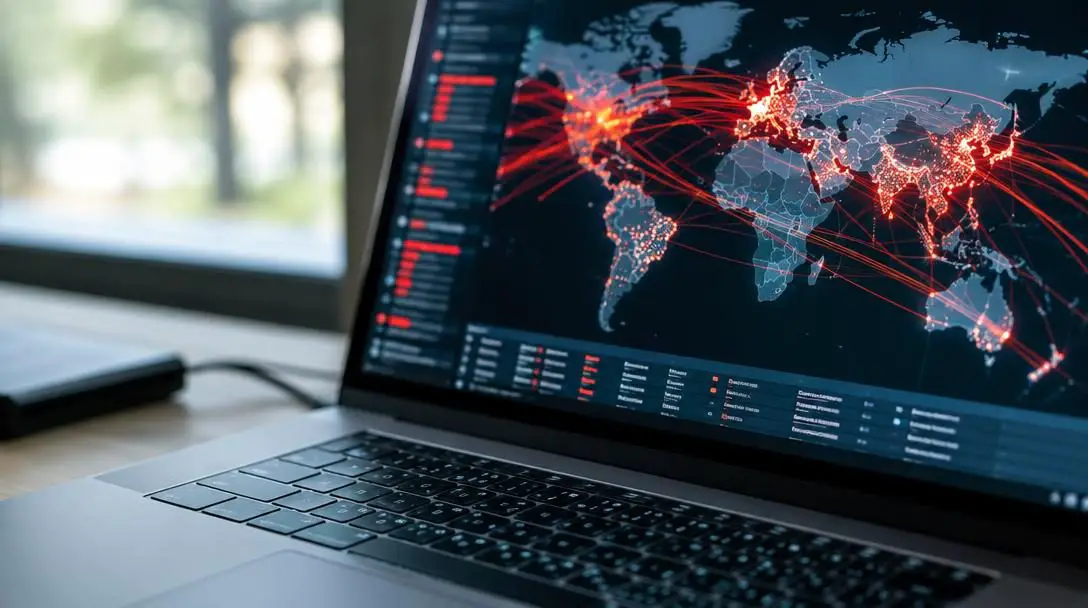
To prepare an assault, perpetrators exploit systems with known, unpatched software vulnerabilities, administrative oversights, or existing malware infections. These hijacked nodes can include remote cloud servers, unsecured desktop workstations, and internet-connected devices. The owners of these compromised units generally observe no obvious behavioral changes, entirely unaware that their hardware has been co-opted to act as a launch pad for future network strikes.
Transmitting the Central Command
Once an attacker selects an administrative target, centralized instructions deploy across the assembled fleet of infected machines. The hijacked machines simultaneously fire directed streams of dummy requests toward the target's IP address, domain registry, or hosting infrastructure. Because these requests arrive concurrently from thousands of disparate origin points around the world, filtering out bad data through simple address blacklisting becomes exceptionally difficult.
Saturating Hardware and Bandwidth Limits
Every web host relies on finite computational power, volatile memory, and network pipeline limits. As malicious data packets arrive in torrents, the server expends its system resources attempting to parse headers, acknowledge incoming handshakes, and return requested resources. Within moments, internal request queues back up, processing threads lock up, and server memory buffers exhaust their limits under the unnatural strain.
Triggering Complete Service Disruption
With computational resources entirely consumed, the host drops incoming connection requests. Genuine users attempting to browse web content, process shopping carts, or query database records encounter loading screens that eventually terminate in standard network timeouts. The target platform remains effectively isolated from the legitimate internet until the incoming flood is deflected or filtered.
Recognizing the Operational Signs of an Active Attack
Early identification of an incoming flood allows administrative teams to initiate defensive protocols before downtime triggers extended financial damage. Because volumetric assaults masquerade as legitimate spikes in visitor interest, diagnosing system telemetry carefully is essential.
Extreme Loading Delays
The earliest symptom of an unfolding incident is an abrupt, system-wide degradation in responsiveness. Pages that normally render in milliseconds stall indefinitely while database lookups and static assets struggle to load over congested ports.
Total Site Unavailability
When computational limits are completely breached, host servers cease responding to external web browsers. Instead of displaying landing pages or interactive portals, web browsers return explicit gateway timeouts, internal server failures, or missing host alerts.
Inconsistent Regional Access Reports
Platform operators often remain unaware of an active outage because locally cached assets or internal network routings allow internal staff to view the website normally. Meanwhile, external visitors, remote teams, and global monitoring systems report that the platform is completely inaccessible.
Collateral Communication and Database Failures
Because web applications often share underlying server infrastructure with internal communications, a volumetric flood against a web address rarely impacts public pages alone. Connected platforms, including web-hosted email accounts, private database endpoints, and employee portals, frequently crash in tandem with the primary public domain.
| Warning Sign | Underlying System Cause | Direct User Experience |
|---|---|---|
| Extreme Loading Delays | Processing queues and memory buffers operating at absolute capacity | Unresponsive interfaces, stalled browsing, and unfinished page rendering |
| Gateway Timeouts | Web server fails to receive upstream response before connection limit expires | Explicit browser error alerts instead of requested web pages |
| Asymmetrical Access | Local browser caching masks network pipeline saturation affecting outside traffic | Platform appears stable internally while outside visitors cannot connect |
| Secondary Service Halts | Shared server resources overwhelm connected databases and hosted email daemons | Bounce-back emails, failed portal logins, and interrupted background tasks |
A Step-by-Step Guide to Strengthening Server Defenses
While absolute immunity against malicious online operations is impossible, executing a structured technical strategy significantly dampens the blast radius of volumetric campaigns. Implement the following sequence to enhance defensive resilience across your web operations.
- Select protected hosting infrastructure: Deploy your applications on hosting platforms that provide baseline denial of service safeguards as part of their standard operational service tiers.
- Upgrade defensive filtering capacities: Because modern operations scale to hundreds of gigabytes per second, upgrade your protection tiers to ensure your upstream host can scrub massive volumetric anomalies before they reach your server.
- Draft an immediate incident escalation plan: Compile internal contact rosters and establish pre-authorized support escalation channels with your host so technical teams can inspect incoming traffic logs without administrative delays.
- Implement distributed load-balancing systems: Disperse incoming traffic across multi-node server clusters rather than directing all traffic toward an isolated machine, preventing single points of infrastructural failure.
- Maintain routine software patch cycles: Apply security updates and patch dependencies across your operating system, web servers, and third-party administrative utilities to keep attackers from hijacking your own assets.
Common Misconceptions and Costly Security Mistakes
Navigating cybersecurity emergencies requires clear technical thinking. Avoiding typical procedural blunders keeps administrators from exacerbating a service outage:
- Assuming small entities are ignored: Overlooking protection because an organization lacks high-profile visibility is a critical misstep. Threat actors routinely attack small enterprises, educational bodies, and regional non-profits whenever an unpatched hole presents itself.
- Relying exclusively on legacy software: Trusting unmanaged, local protection scripts to repel high-bandwidth assaults creates a dangerous illusion of security when volumetric floods exceed hosting pipeline limits.
- Delaying technical provider outreach: Waiting several hours to contact hosting engineers allows traffic floods to cascade across secondary network systems, compounding operational disruption.
- Confusing network floods with viral popularity: Mistaking an abnormal spike in raw server inquiries for organic marketing growth delays crucial defensive intervention until physical servers have crashed.
Frequently asked questions
What does the term DDoS stand for?
DDoS stands for distributed denial of service, a method of cyberattack where numerous compromised computer systems coordinate to overwhelm a target server with illegitimate network traffic.
Why do attackers target smaller organizations and non-profits?
Attackers do not restrict their targets to massive global enterprises; they routinely probe the web for any accessible vulnerability, striking small non-profits and modest websites simply because unpatched software or weak defenses make them vulnerable.
How can a website appear functional to an owner while remaining down for visitors?
Local browsers frequently store cached versions of website assets, allowing site owners to view pages smoothly even while incoming network pipelines are saturated and remote visitors are barred from loading the site.
Can standard software tools stop modern large-scale traffic floods?
Standard standalone software utilities often fail against modern attacks because current assaults routinely reach several hundred gigabytes per second, a volume that requires upstream network scrubbing and robust hosting infrastructure to manage.
What should an administrator do first when an attack is suspected?
The priority is to execute an established incident response plan by contacting your hosting provider immediately, enabling network engineers to analyze traffic logs and deploy traffic redirection or scrubbing mechanisms.
The Bottom Line
Distributed denial of service operations have evolved into an enduring fixture of the modern threat landscape, presenting persistent risks to any individual or enterprise operating an online property. As automated botnets expand and volumetric strikes regularly eclipse several hundred gigabytes per second, maintaining a purely reactive security posture is no longer viable. The staggering financial toll—such as the $3.5 million hourly losses reported among top eCommerce platforms during major server failures—highlights the vital necessity of continuous infrastructure readiness.
Protecting your online footprint demands an active, multilayered approach. By pairing upgraded hosting tiers with distributed load balancing, timely patching, and rapid escalation procedures, you can safeguard your critical infrastructure against unexpected traffic surges. Combining operational availability strategies with rigorous safeguards for user payment records, personal profiles, and Social Security data ensures that your platform remains resilient, trustworthy, and consistently accessible to legitimate users.